
Exaforce MDR: Expert-led,
platform-powered, AI-accelerated
A fully-managed SOC that adapts to your business, combining the depth and scalability of AI with the expertise of seasoned analysts.
Trusted by leading security teams


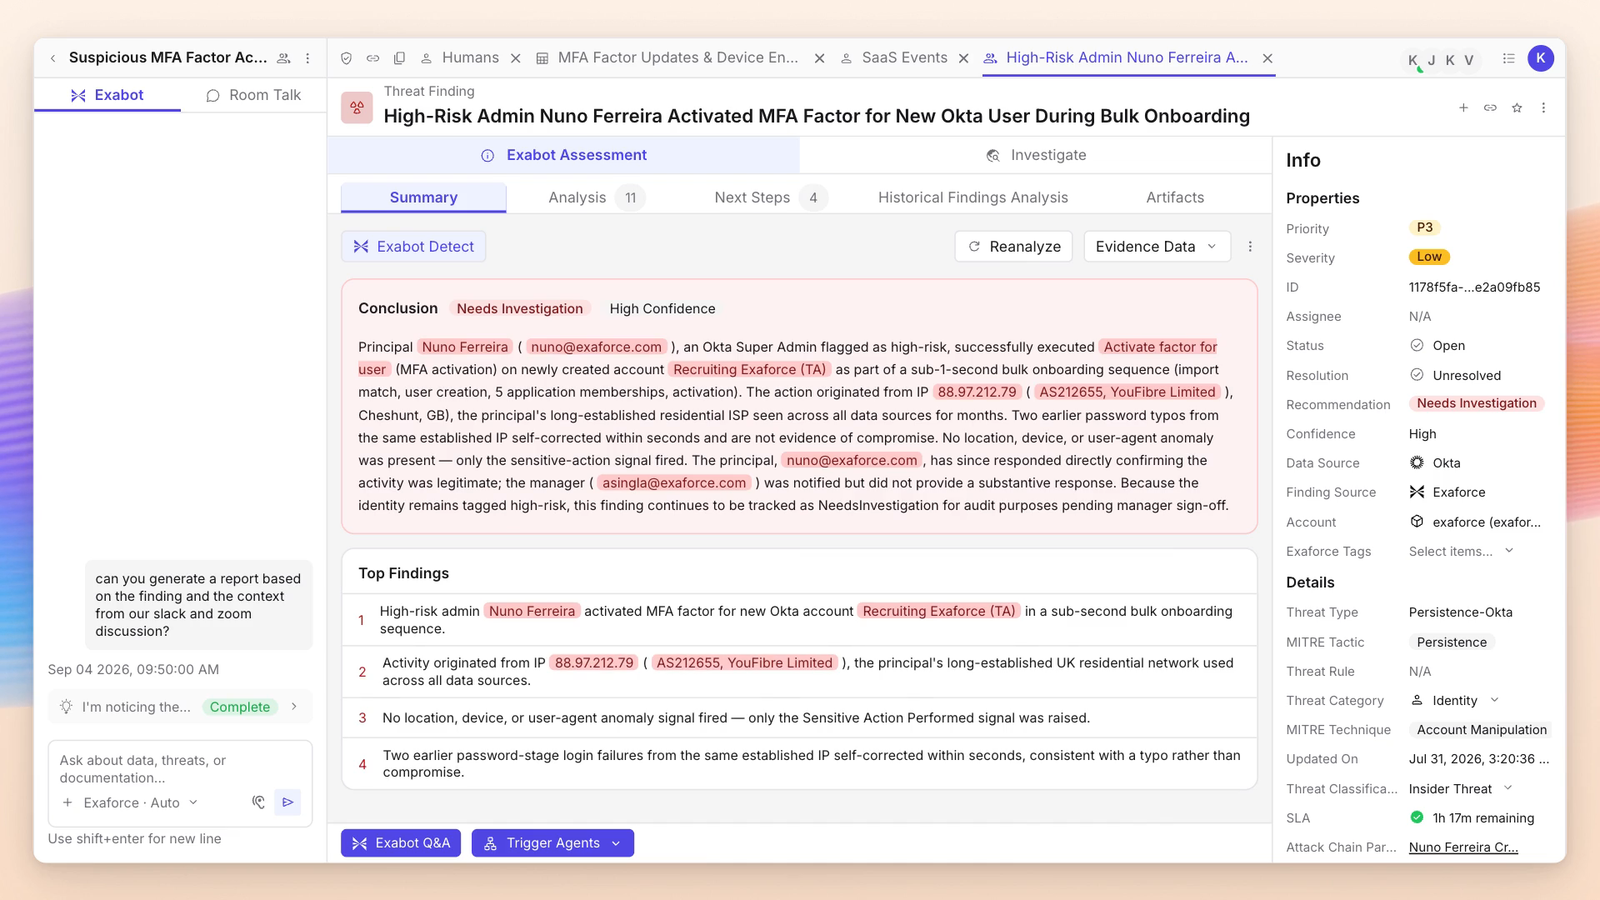
- 250Kalerts investigated in the last 90 days
- 0.06%escalation rate
- 7 minmean time to investigate (MTTI)
- <30 minaverage time from alert to response
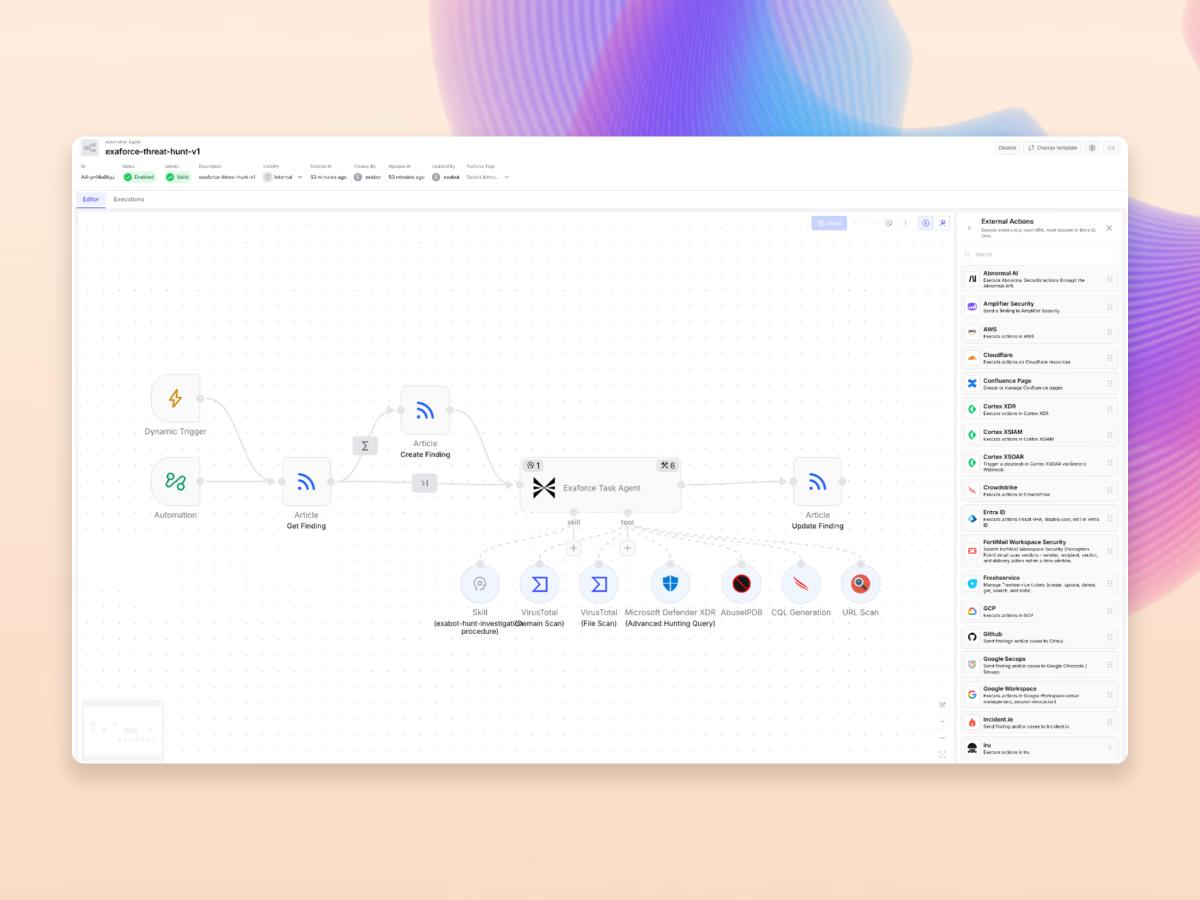
Traditional MDRs work through alert queues by hand. Exabots triage in seconds, then a library of 200+ dynamic actions contain the threat at machine speed, with expert oversight.
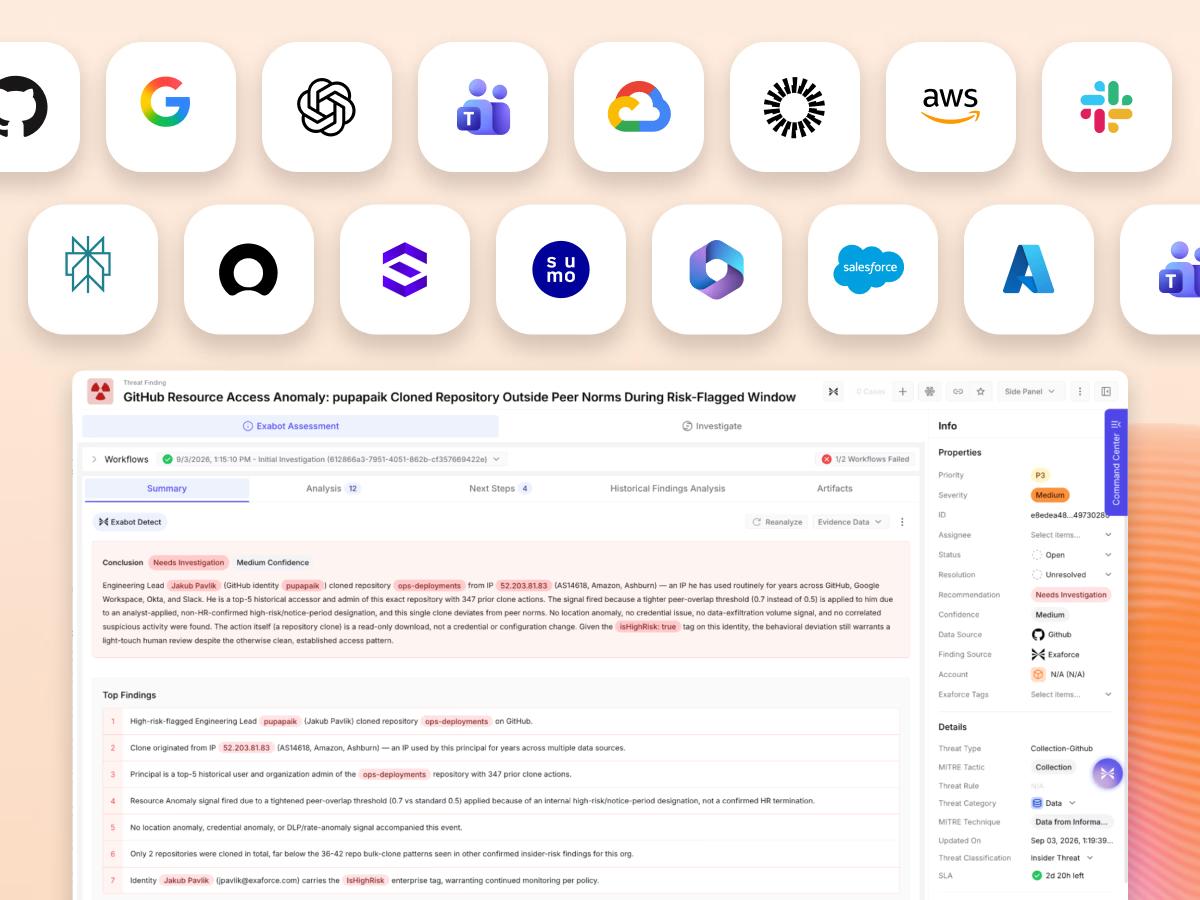
Every single alert gets ingested, triaged, and analyzed thoroughly. From all sources (over 120 supported), all priorities. No gaps, nothing is too insignificant.
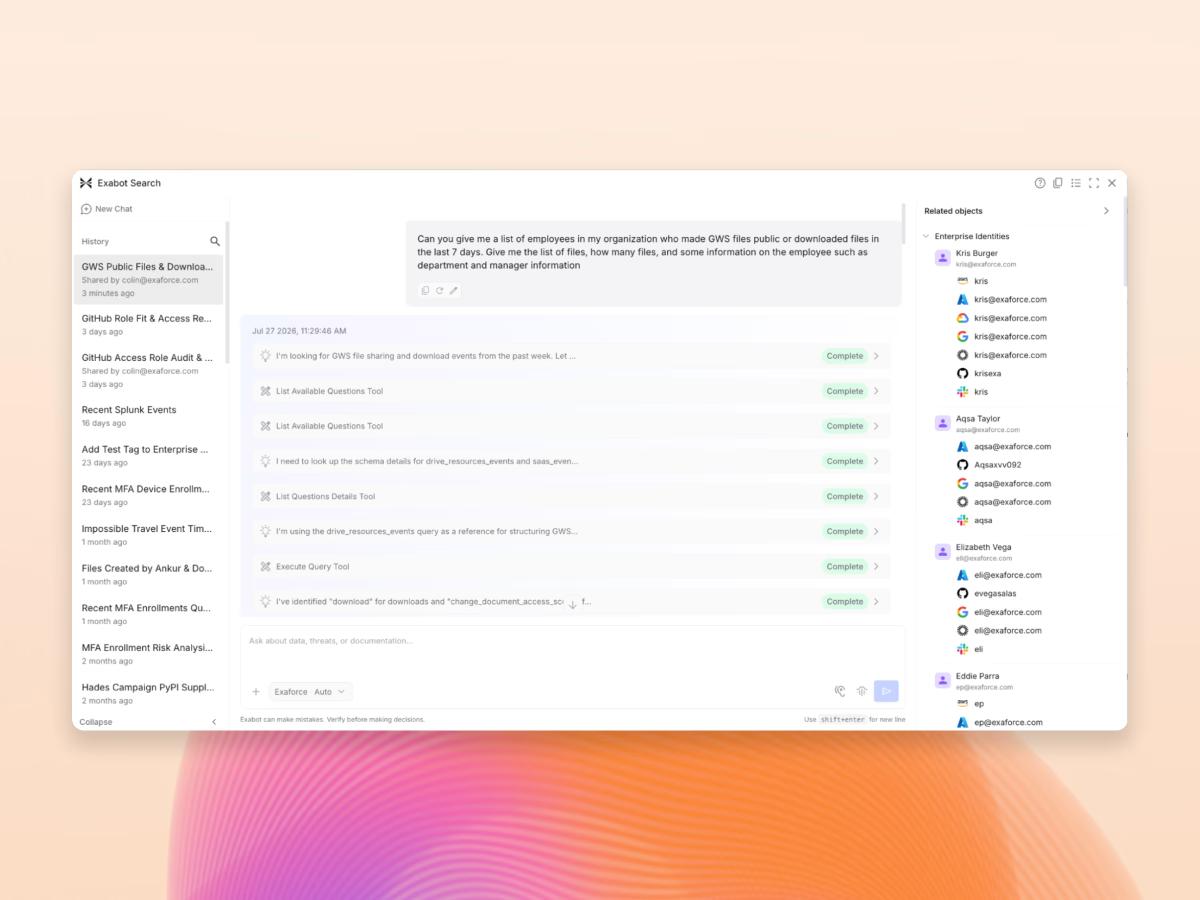
There is no analyst-only back end. Every data source, investigation, dashboard, and automation our team uses is yours to open, query, and change. Got a question? Ask Exabot in plain language instead of waiting on a call. And if you ever bring the team in house, you keep the platform.
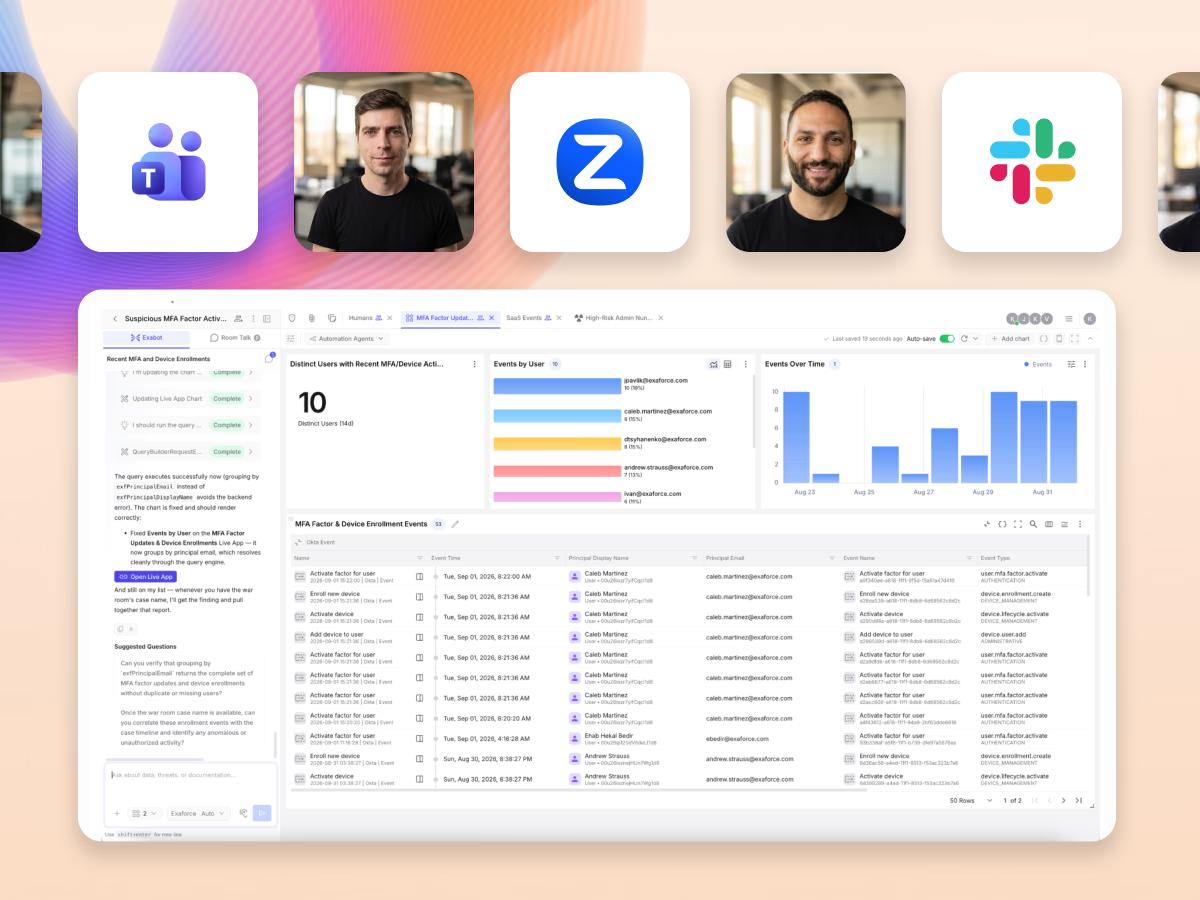
Collaborate in a war room, not a thread
A collaboration space built on top of the data. Investigate in parallel or side by side with our analysts, share dashboards, spin up a Slack channel or a Zoom, and every message, decision, and artifact stays centralized with the evidence, ready to report on or ask Exabot about.
Collaborate in a war room, not a thread
A collaboration space built on top of the data. Investigate in parallel or side by side with our analysts, share dashboards, spin up a Slack channel or a Zoom, and every message, decision, and artifact stays centralized with the evidence, ready to report on or ask Exabot about.
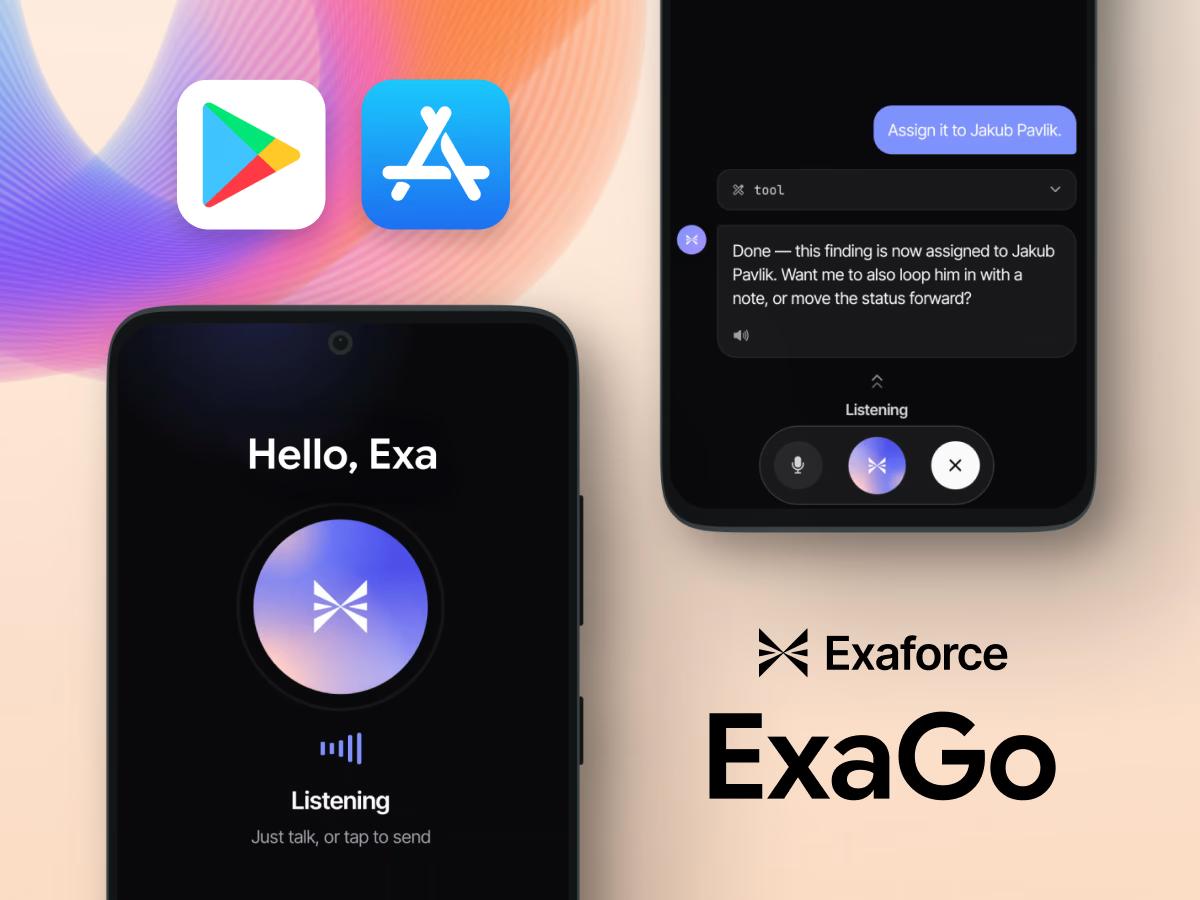
Unshackle yourself from the desk with ExaGo
The same console, on your phone. Get notifications, review an escalation, ask a question, and approve or trigger a response action from wherever you happen to be
Unshackle yourself from the desk with ExaGo
The same console, on your phone. Get notifications, review an escalation, ask a question, and approve or trigger a response action from wherever you happen to be
One platform, not eight tools
MDR runs on the same platform as everything below it, so detections, investigations, response, and review all share one data set and one audit trail.
SIEM
A security data lake with search, detection, and retention, with none of the tuning overhead.
Risks
Standing exposure and insider risk for all your Cloud and SaaS sources. Tracked continuously.
Access reviews
Access review campaigns driven by the same identity data and permission modeling your detections use.
Reports
Executive and SOC reporting built from live investigation data, available on demand.
AI security
Visibility and controls for AI services, agents, and the identities they act through.
SOAR
Built-in automated response with a library of 200+ out-of-the-box actions.
AI SOC
Exabots that triage, investigate, and document every alert end to end.
MDR
Our analysts running all of the above for you, 24/7, on the same platform you log into.
What makes our MDR better
Breakthrough AI paired with advanced data exploration for higher quality outcomes, faster and cheaper.
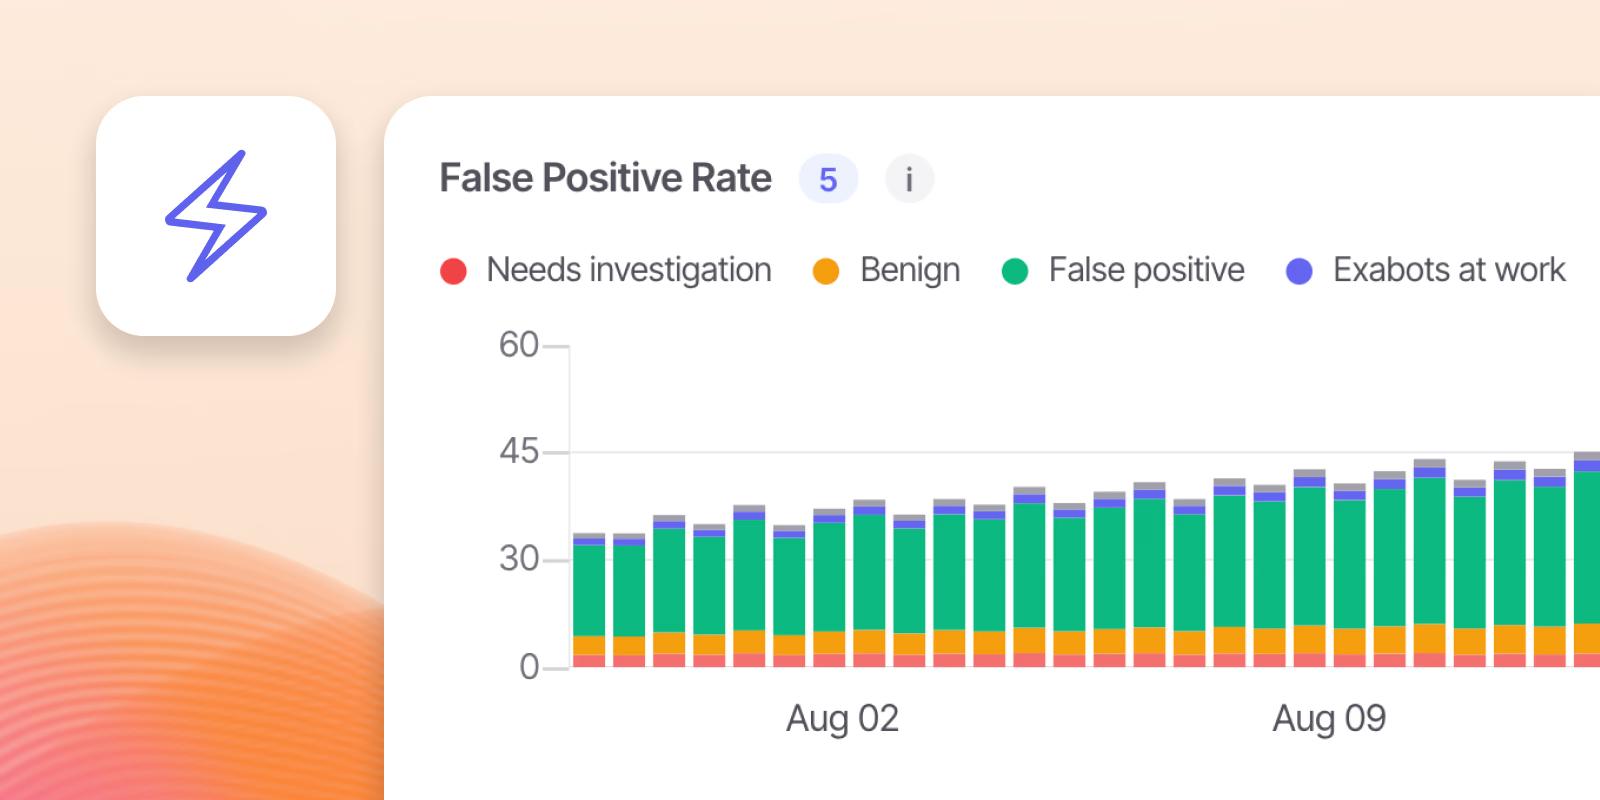
Better
Our multi-model AI connects identity, config, and code—not just logs—and learns with every decision. You stay in control, with no false-alarm wake-ups.
“We went from an MSSP that needed hand-holding to an MDR that handles investigations we never could before.”
 Guy Shamilov, CISO at Forcepoint
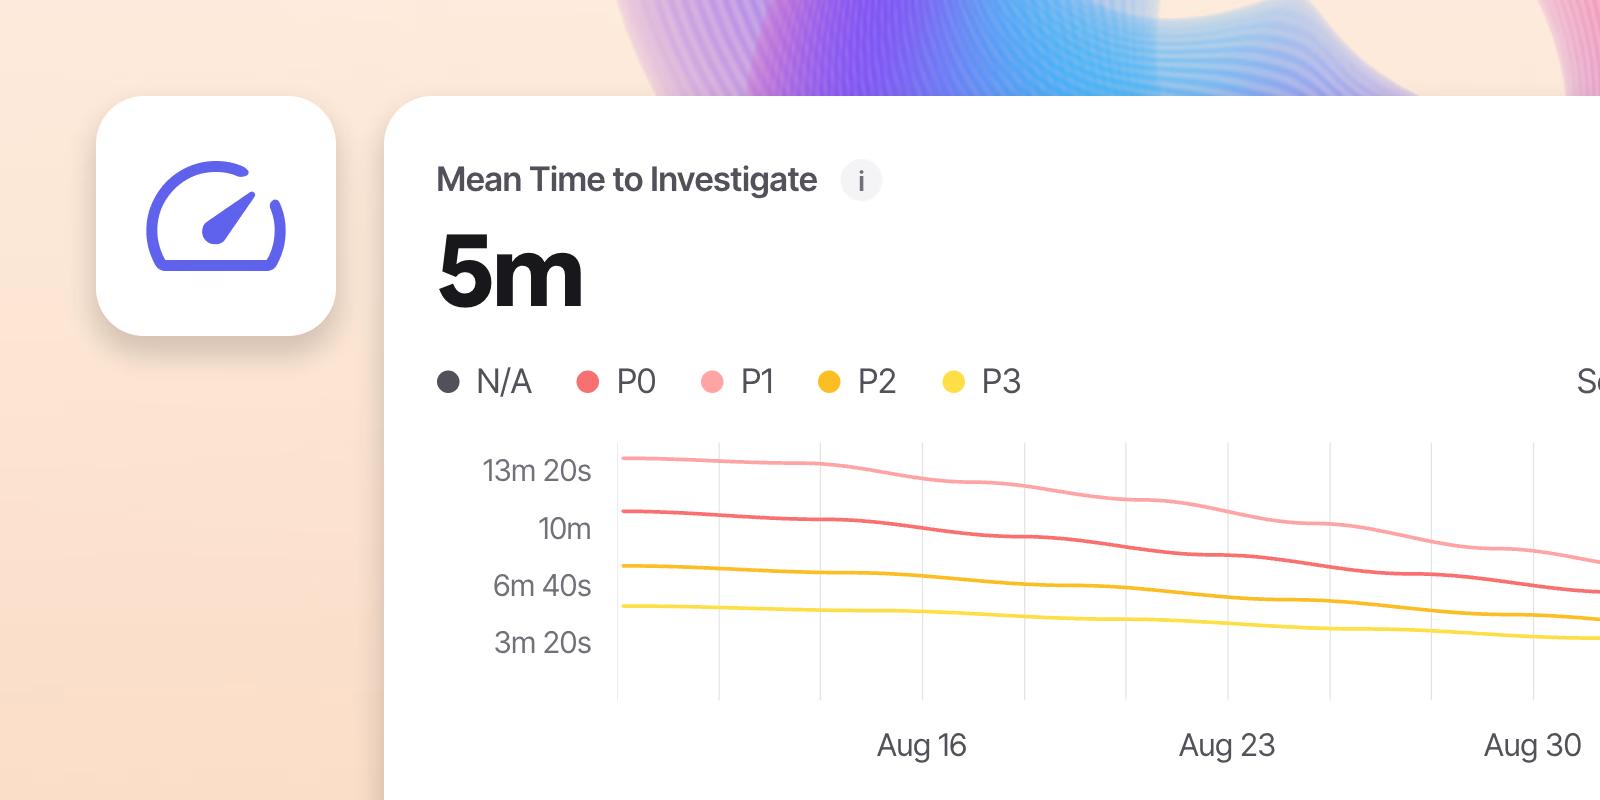
Faster
Exabots triage, investigate, and respond in real time, 24/7, with expert oversight. Every threat addressed, none missed.
“The time to detect, contain, and respond to incidents has gone from hours or days to minutes.”
 Corey Roop, Director of Production Security at Invisible Technologies
Cheaper
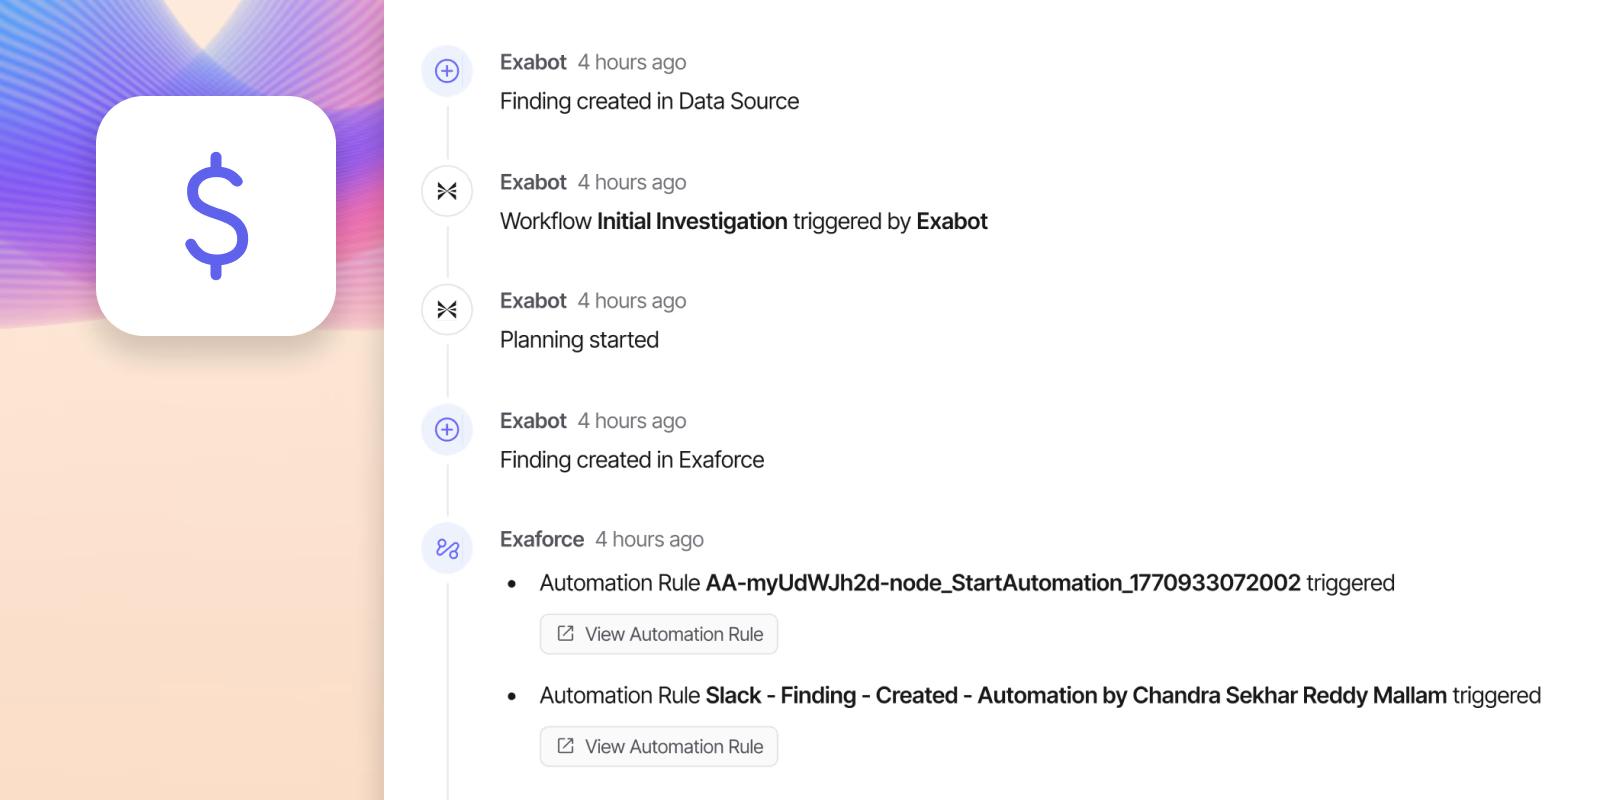
10x your team throughput without the cost. AI offloads the busywork, so your team can maximize their capacity and scale with your business.
“Everything we’ve done since Exaforce came in, the efficiency has gone up at least 10x.”
 Patrick McKinney, VP of Security
Related resources
Evaluate your AI SOC initiative
A maturity mapped question framework to benchmark AI SOC platforms on detection, triage, investigation, response, and service quality.
Webinar: “What is AI SOC” Anyway?
Cutting through the hype with James Berthoty (CEO & Principal Analyst, Latio) and Taylor Smith (Director of Product, Exaforce)
Latio AI Security Market Report 2025
Get actionable insights about the latest developments in AI security. Written for both security leaders and engineers, this report covers the state of the market, leading use cases, and what vendor innovations.